The Unofficial HackTheBox Web Exploitation Expert (CWEE) Study Notes
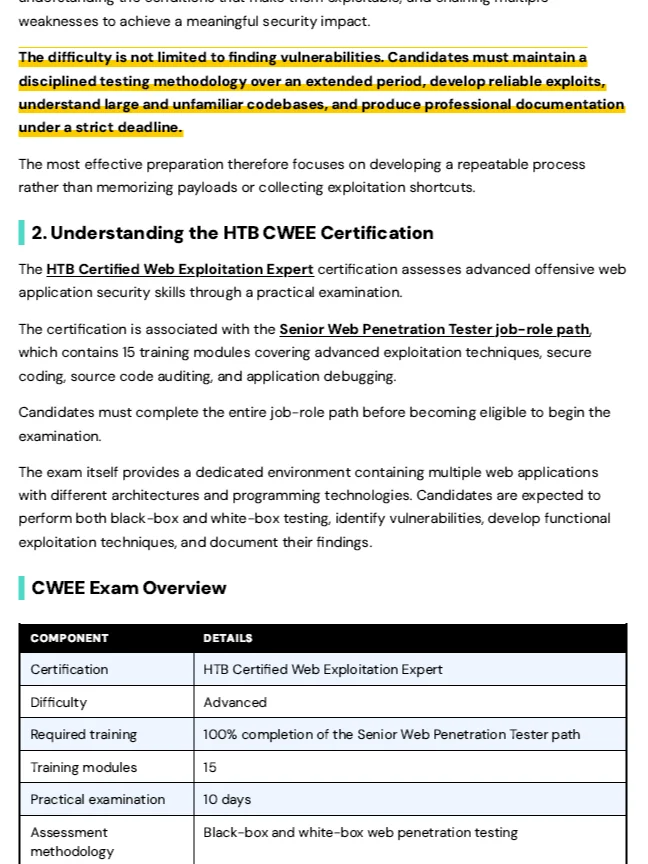
The HTB Certified Web Exploitation Expert certification assesses advanced offensive webapplication security skills through a practical examination.
The certification is associated with the Senior Web Penetration Tester job-role path,
which contains 15 training modules covering advanced exploitation techniques, securecoding, source code auditing, and application debugging.
Authored and reviewed by certified professionals with firsthand experience preparing for and earning the certification.
Who Is It For
- Senior penetration testers
- Web application penetration testers.
- Application security engineers
- Frontend and backend developers
- Source code security reviewers
- Experienced bug bounty hunters
Table of Contents:
- HTB CWEE Exam Preparation
- Modern Web Exploitation Techniques
- DNS Rebinding
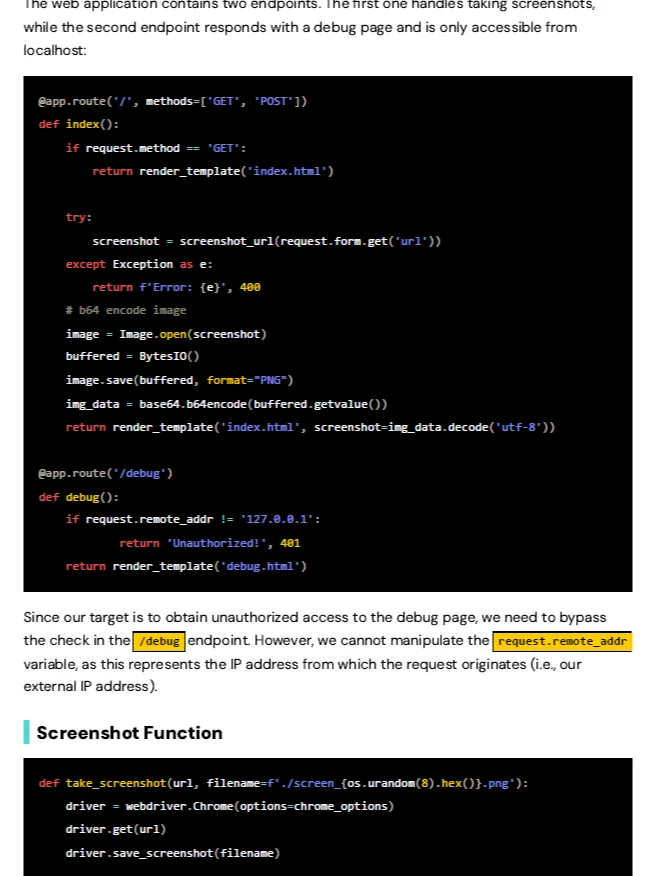
- SSRF Basic Filter Bypasses
- Second-Order Web Attacks
- Second-Order Command Injection
- Second-Order IDOR (Blackbox)
- WebSocket Attacks
- XPath Injection
- XPath Authentication Bypass
- XPath Advanced Data Exfiltration
- XPathBlind Exploitation
- XPath Injection Prevention & Tools
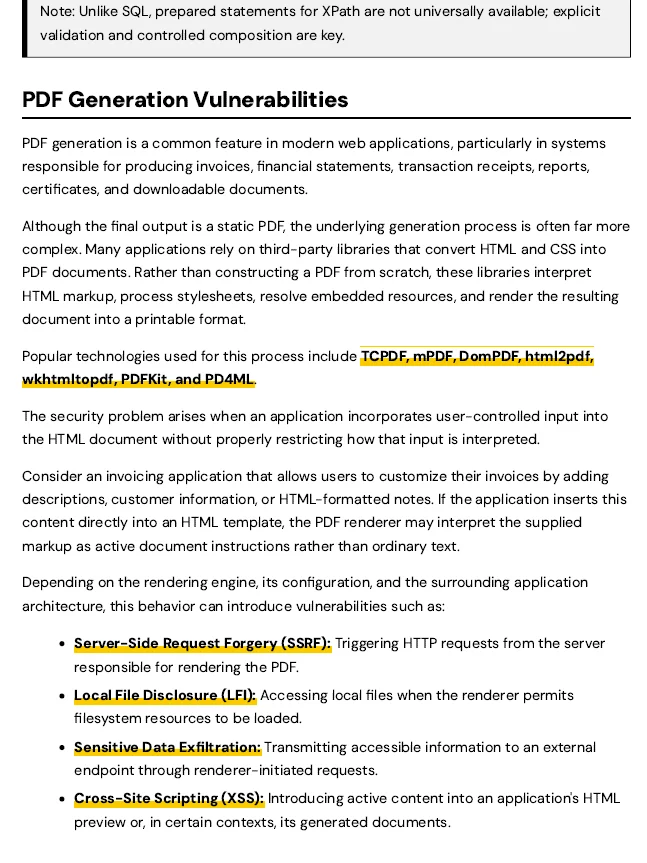
- PDF Generation Vulnerabilities
- Exploitation of PDF Generation Vulnerabilities
- Prevention of PDF Generation Vulnerabilities
- LDAP Injection
- LDAP - Authentication Bypass
- LDAP - Data Exfiltration & Blind Exploitation
- LDAP Injection Prevention
- NoSQL Injection
- Authentication Mechanisms
- Server-Side JavaScript Injection
- Attacking JWT Signature Verification
- Attacking the JWT Signing Secret
- Algorithm Confusion Attack (JWT)
- Further JWT Attacks & Header Claim Exploitation
- JWT Tools of the Trade & Vulnerability Prevention
- OAuth
- Stealing Access Tokens via OAuth Misconfigurations
- Improper CSRF Protection in OAuth (The state Parameter)
- Additional OAuth Vulnerabilities
- OAuth Vulnerability Prevention
- SAML
- Signature Exclusion Attack
- Advanced CSRF & XSS Exploitation
- Same-Origin Policy and CORS
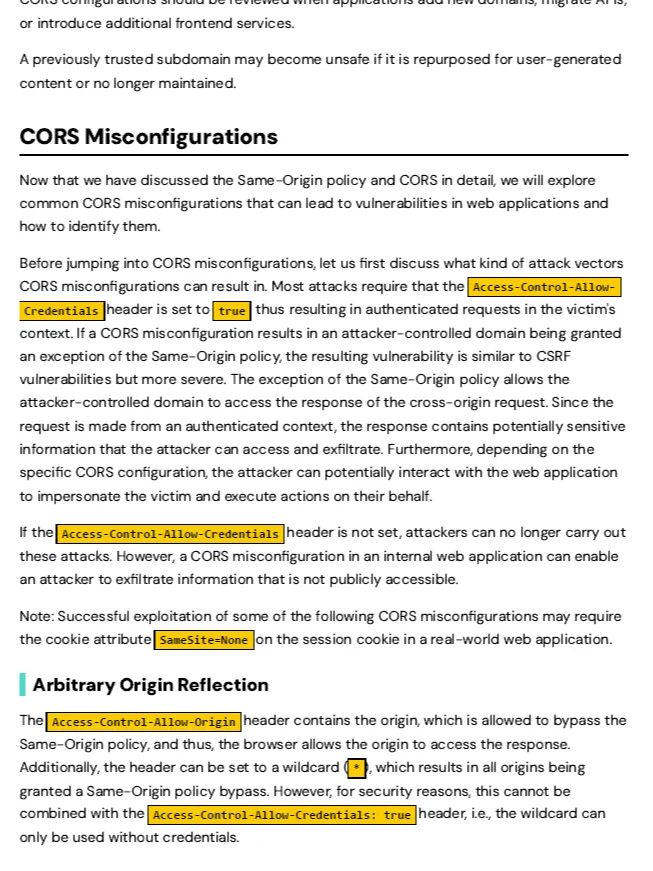
- CORS Misconfigurations
- Cross-Site Request Forgery (CSRF) Vulnerability Prevention
- Misc CSRF Exploitation
- XSS Exploitation
- Enumerating Internal APIs
- Exploiting internal Web Applications II
- Content Security Policy (CSP)
- Bypassing Weak CSPs
- XSS Filter Bypasses
- Cross-Site Scripting (XSS) Vulnerability Prevention
- Launching Attacks from the Victim's Session
- HTTP Misconfigurations
- Web Cache Poisoning
- Host Header Attacks
- Web Cache Deception
- Web Cache Poisoning
- Handshake Overview
- TLS 1.3
- Public Key Infrastructure
- What is Padding?
- Padding Oracles
- POODLE & BEAST
- Bleichenbacher & DROWN
- Heartbleed Bug
- Cryptographic Attacks
- Downgrade Attacks
- Testing TLS Configuration
- Introduction to MSSQL/SQL Server
- Introduction to Blind SQL Injection
- Identifying Boolean-based SQLi
- Designing the Oracle
- Optimizing Blind SQLi
- Time-based SQLi
- Time-based Oracle Design
- Time-based Data Extraction
- Out-of-Band DNS Exfiltration
- MSSQL Remote Code Execution
- MSSQL File Read
Page Count: 764
Format: PDF
Usage Notes:
- The unofficial study notes
- QAs
Disclaimer: Unofficial Study Material
This study guide is an unofficial, independently written resource created solely for educational purposes. It is based on personal exam experience and publicly available information. This product is not affiliated with, endorsed by, or authorized by The certification body, or any of their partners. It does not contain any copyrighted material, proprietary courseware, or confidential exam content.All trademarks, logos, and brand names are the property of their respective owners. By purchasing or downloading this material, you agree not to hold the author or this store liable for any outcomes related to exam performance.
Note: This product is not eligible for a refund.
If you have concerns regarding the product, kindly contact consultation@motasem-notes.net and clarify your issue and explain why the eligibility for a refund.