The Ultimate Blue Team & Cloud SOC Analyst Bundle
Master Threat Detection, SIEM, Incident Response, Threat Hunting & Multi-Cloud Security Across AWS, Azure and GCP.
The Ultimate Blue Team & Cloud SOC Analyst Bundle brings together two extensive technical manuals covering traditional blue-team operations and modern cloud security investigations, providing more than 2,500 pages of cybersecurity knowledge, practical commands, detection techniques, investigation workflows, and real-world security scenarios.
What's Included?
Book 1: The Definitive Blue Team Manual
Your comprehensive reference for defensive cybersecurity and Security Operations Center operations.
Explore the technologies, workflows, and investigation techniques used by blue-team professionals.
Key topics covered:
-
SOC Operations: SOC architecture, analyst responsibilities, alert triage, incident handling, and operational playbooks.
-
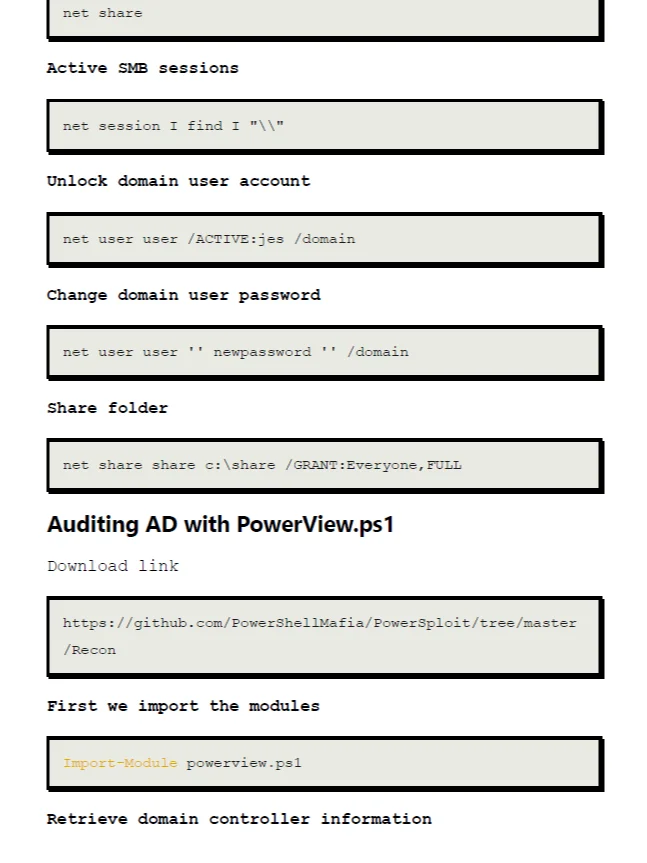
SIEM & Security Monitoring: Splunk, Elastic Stack, Wazuh, log ingestion, detection queries, dashboards, and alert management.
-
Network Security & Traffic Analysis: Wireshark, TCPdump, Tshark, Zeek, Snort, and Suricata.
-
Threat Hunting & Incident Response: Threat intelligence, forensic investigation, malware detection, containment, and remediation.
-
Detection Engineering: Sigma and YARA rules, intrusion detection signatures, endpoint monitoring, and practical detection use cases.
-
Advanced Security Topics: Vulnerability management, reverse engineering, secure coding, and AI security concepts.
Book 2: The Cloud SOC Field Guide (Cloud SOC Analyst Manual)
Extend your defensive security skills into AWS, Microsoft Azure, Google Cloud, containers, and cloud-native infrastructure.
Learn how security analysts investigate cloud threats through native logging services, command-line tools, SIEM integrations, and structured investigation workflows.
Key topics covered:
-
Multi-Cloud Security: AWS, Azure, and Google Cloud security architecture, IAM, permissions, and monitoring.
-
Cloud Investigation & Forensics: AWS CLI, Azure CLI, gcloud, CloudTrail, CloudWatch, Microsoft Sentinel, KQL, and jq.
-
Cloud Threat Detection: Credential theft, token replay, MFA fatigue, federated identity abuse, OAuth application attacks, and privilege escalation.
-
Cloud SIEM Integration: Collecting and correlating AWS, Azure, and GCP logs through Splunk and cloud-native security platforms.
-
Container & Kubernetes Security: Docker security, Kubernetes audit logs, runtime threat detection, container forensics, and hardening.
-
Advanced Cloud Incident Response: Identity-based threat hunting, data exfiltration investigations, Infrastructure-as-Code security, and CI/CD pipeline compromises.
-
Career Preparation: Cloud SOC interview questions, investigation scenarios, and technical reference material.
What You Receive
-
2 digital cybersecurity manuals (PDF)
-
2,400+ pages of combined technical content
-
Coverage of traditional, hybrid, and cloud security operations
-
Practical commands, investigation workflows, detection examples, and case studies
-
Technical reference material spanning SOC fundamentals through advanced cloud security